
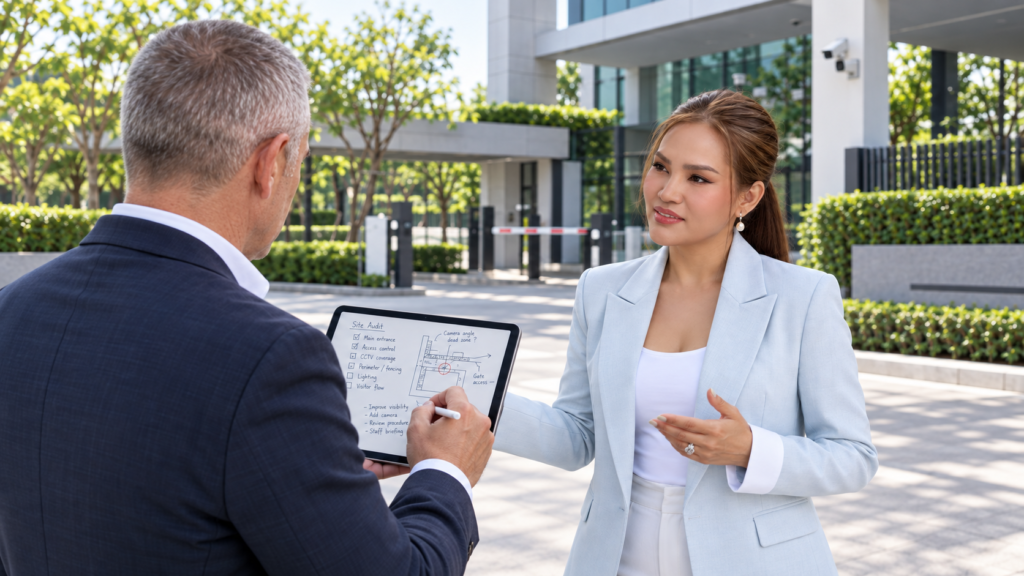
Identifying Vulnerabilities, Improving Security
Identifying Vulnerabilities, Improving Security
A security audit identifies vulnerabilities that could allow an intrusion, unauthorised movement or a malicious act to take place within or around a site.
Intrusion is naturally a central aspect of the analysis, as is the risk posed by someone who is legitimately authorised to enter the premises. It may result from a violent or premeditated act, but equally from a missing, misunderstood, or inadequately enforced rule. The audit therefore considers all vulnerabilities affecting the site, with particular attention paid to its perimeter, the first line of protection against intrusion, and to its internal alert system.
One Site May Contain Several Sites
A facility does not necessarily constitute a single, uniform security environment. Certain areas may be particularly sensitive and therefore require their own conditions of access, movement and operation.
A research and development department, for example, may be treated as a site within the site. The audit examines the coherence of this security zoning, the protection afforded to each area and the interactions between the different zones. A person authorised to enter the facility is not necessarily authorised to access every part of it.
This is the purpose of security zoning: each zone may be governed by more specific internal rules, together with appropriate arrangements for movement and interaction between zones.
Observing Security Under Real Operating Conditions
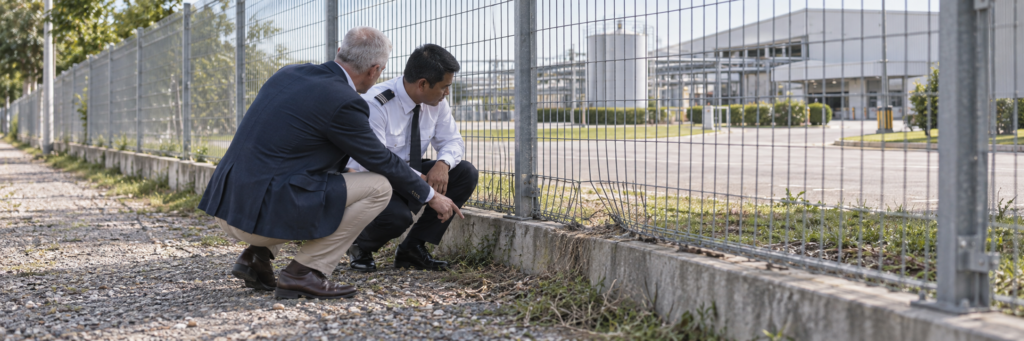
The analysis considers the human, technical and organisational resources contributing to security, including the perimeter, access control, CCTV, security rounds, patrols, instructions and procedures. These elements are not examined in isolation. The objective is to assess their overall coherence and how they operate under the site’s actual working conditions.
The audit may reveal shortcomings, but it may also confirm that the existing arrangements are appropriate. It can also lead to their simplification where certain measures have become excessively restrictive, redundant or costly. Well-designed security must provide effective protection without unnecessarily obstructing operations.
From Findings to Solutions
An audit should not merely identify vulnerabilities. It must propose realistic responses, establish priorities and enable the client to assess the operational and financial implications of the recommended measures.
Where necessary, we create or update operational procedures to translate recommendations into rules everyone concerned understands and can apply.
At SDS, our audits are not based on a simple checklist. Each assignment is designed around the site’s activities, environment and particular constraints. The site visit is only the visible part of the process: **one day in the field generally represents two additional days of analysis and report writing.