Beyond the “Site Survey”
This page is not about a standard site survey used primarily as
a commercial tool to prepare a guarding proposal.
It is about professional Security Audits and Risk Assessments
conducted as genuine security consultancy assignments.
Our work follows a structured methodology: identifying and
analysing threats, vulnerabilities, and operational consequences;
formulating practical, proportionate, and accountable
recommendations; and, eventually, developing the financial schedule.
A site survey observes a location. An audit examines the security system
as a whole and assesses the responsibilities of those who oversee it.
Why an audit matters
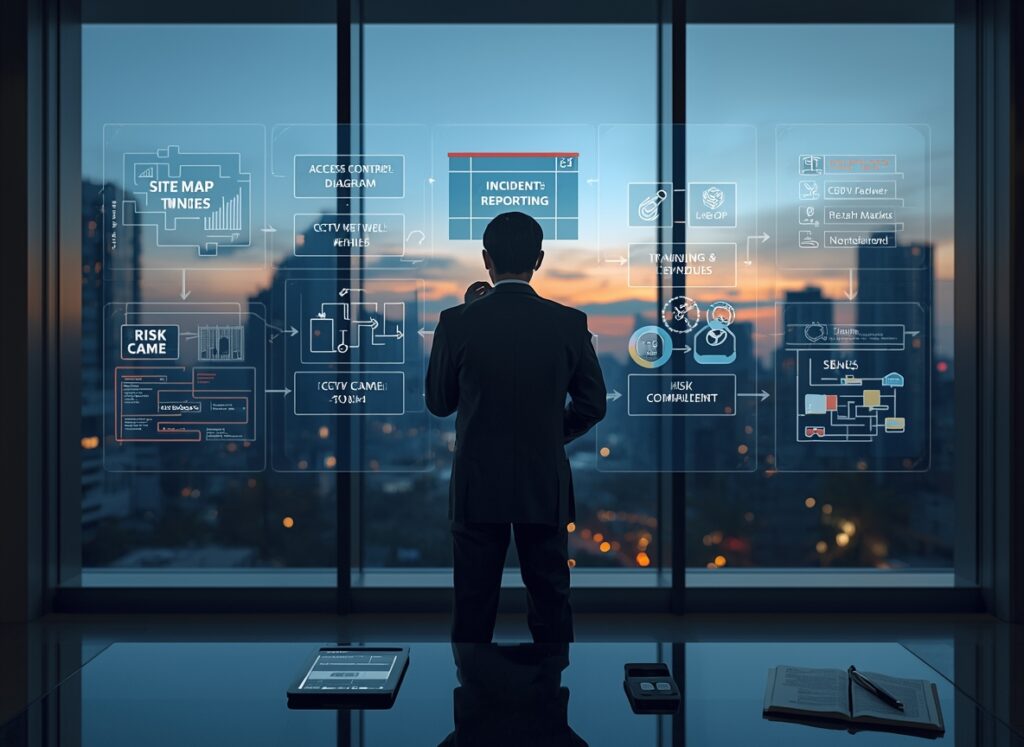
Many security failures stem from incorrect assumptions: unclear priorities, blind spots in daily routines, underestimated vulnerabilities, and weak escalation discipline. A structured audit reduces uncertainty and supports rational decision-making. It also ensures that any future deployment, human or technological, aligns with actual needs rather than habits or impressions.
Many assessments on the market are tied to predefined solutions. Our approach is different: we start with the site, the operations, and the risk reality, then we build the most feasible plan.
Our audit approach
SDS conducts audits through a precise sequence.
1 Site walkthrough and operational mapping
2 Vulnerability review
3 Discovery and objectives
4 Threat scenarios and prioritisation
5 Recommendations and operating model
6 Financial scheduling
1
We evaluate the site based
on operational realities: access points, perimeter logic, reception routines, delivery flows, visitor movements, peak times, shift changes, and critical zones.
This step is essential because security must reflect how a site operates in reality, not how it appears on paper.
2
We identify vulnerabilities that can lead to incidents.
This typically includes access control discipline, visibility and lighting, blind spots, CCTV coverage logic, communication channels, escalation rules, and documentation practices.
We also assess whether the reporting is actionable and supports corrective actions.
3
We confirm your context and expectations: people, property, reputation, business continuity, and operational constraints.
We identify decision-makers and stakeholders, then define the scope, timeline, and the required level of confidentiality.
4
Security is not meant to block work; it is intended to enable a safe environment in which people can operate with confidence.
Together, we define likely scenarios for your environment, rank them by probability and impact, and allocate resources accordingly.
A good plan addresses the right risks in the proper order, not necessarily in the order of the longest list.
5
Based on findings, SDS proposes an operating model that is practical and sustainable. This may include shift structure, staffing levels, post duties, critical tasks, required skills, and reporting lines.
If equipment or systems are relevant, we propose a phased approach with priorities and a realistic budget outline. We also define what should be monitored, what should be logged, and how supervision should be conducted.
6
The financial roadmap may be implemented over any suitable timeframe, depending on the organisation’s priorities and available resources.
The first phase addresses critical and immediate security requirements; the second completes compliance and provides a robust level of protection.
The third generally focuses on operational comfort, using technology to simplify processes and improve personnel management.
Deliverables
At the end of the audit, you receive a clear, usable output including a site overview, an operational map, a prioritised list of vulnerabilities, a risk list, a recommended operating model covering shifts, roles, post duties, and reporting lines, your SOP framework outline, training needs with refresh frequency, a practical roadmap with immediate actions, and a 30/60/90-day improvement plan.
When technology is relevant, we address it only as part of the security concept, with an estimate from our genuine partners. We provide training through our Security Academy, EPSA, to align with our recommendations.
Confidentiality
Audit findings are sensitive operational information.
We handle them confidentially and share them only with authorised stakeholders.
Our goal is to provide clarity and practical control without disrupting daily operations.
The audit establishes a solid foundation for long-term security and prevents costly decisions based on assumptions.