
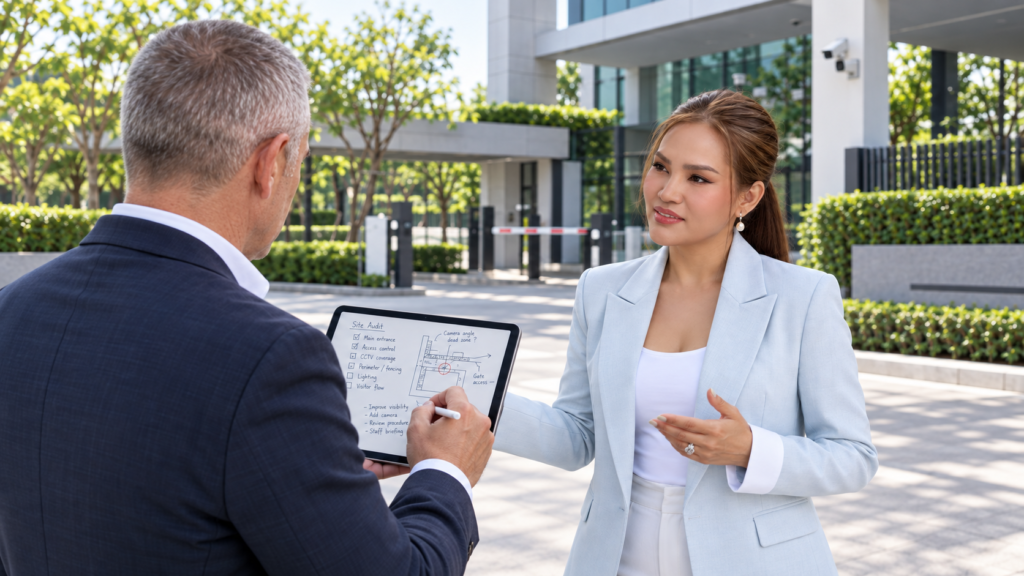
From Documentation to Reality
A compliance audit verifies that the security and crisis management procedures established by a company, group or brand are genuinely understood, applicable and implemented at site level.
The client provides its SOP, security plan, crisis management plan and any other documents forming part of its internal framework. Once these have been reviewed, the auditor develops a compliance matrix to compare the stated requirements with the organisation and practices actually observed on site.
Verifying the Coherence of the Arrangements
The existence of a procedure does not guarantee its implementation.
A document may, for example, require a specific access card to reach a particular floor while the lift continues to serve the entire building without restriction. The rule exists, but the means required to enforce it have never been put in place.
The audit identifies such gaps, along with contradictions, provisions that are no longer relevant and procedures that are too imprecise to be applied. Where the documentation provided is incomplete or lacks operational substance, the first recommendation may simply be to develop a proper SOP before continuing the assessment.
A Crisis Plan Must Be Capable of Working
A crisis management manual may contain dozens of procedures, but the people involved may not know how to use them in practice.
The audit therefore examines the composition of the crisis management team, the allocation of responsibilities and each participant’s ability to fulfil their role. Senior management, security, operations, maintenance, food and beverage, IT or communications may all be involved, depending on the nature of the incident.
Each member does not need to memorise the entire plan. They must, however, understand their responsibilities, know who they need to work with and have access to the information required to act or make decisions. Particular attention is given to the decision-maker and spokesperson, especially where a crisis could affect social media, the organisation’s image, its reputation or its finances.
Assessing, Explaining and Correcting
The audit uses interviews, observations, questionnaires and, where appropriate, a limited exercise. Its purpose is not to catch people out or penalise them, but to assess their knowledge at a particular point in time and identify what needs to be clarified, taught or reorganised.
Where certain gaps can be addressed immediately, the audit may also provide an opportunity for explanation before a further assessment is carried out. Compliance is not merely a score: it must help make the arrangements genuinely usable.
It nevertheless remains a condition observed at a specific moment. Staff changes, transfers and developments within the site therefore require knowledge to be maintained through training, exercises and regular reviews.
A Short and Structured Assignment
Because it is based on an existing framework, a compliance audit is generally faster and more cost-effective than other forms of audit.
Depending on the size of the site and the number of people involved, it usually requires one to two days in the field, followed by approximately one day of analysis and report writing.
The final report presents the requirements reviewed, the gaps identified and the recommendations needed to restore genuine coherence between the documentation, the people involved, the available resources and the site’s actual operation.